Cybercriminals are draining billions from bank accounts with hyper-personalized social engineering schemes, but Google is officially pushing back with Google AI anti-scam protections across the entire Android ecosystem.
- Enhanced Protection Mode: Google Messages introduces an opt-in toggle using cloud-grade Gemini models via Private AI Compute to spot complex, slow-burn conversational scams.
- Smart URL Screening: Next-generation Gemini Nano runs on-device URL analysis in real time to catch freshly registered phishing domains before you tap.
- Call Hijack Blockers: Android will block unauthorized background call forwarding and intercept malicious MMI dialer codes used to siphon one-time passcodes.
- Massive Global Reach: On-device notification scam shields expand across hundreds of millions of devices from brands including Motorola, OnePlus, Xiaomi, and OPPO.
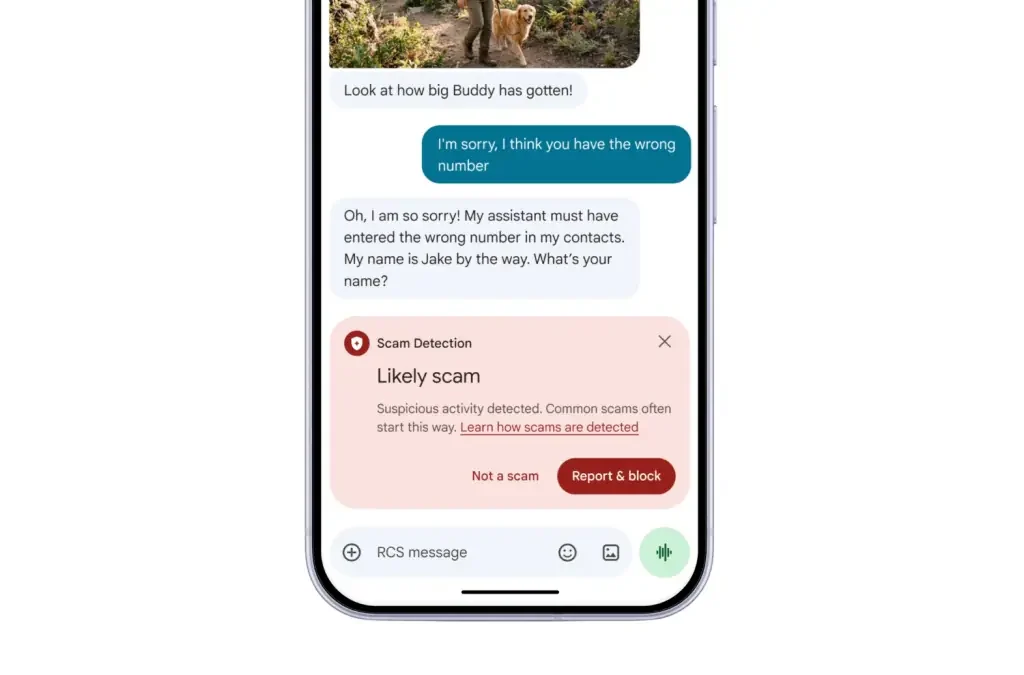
Can automated machine learning genuinely outsmart human manipulators who tailor psychological traps in real time?
Social engineering relies on psychological manipulation rather than traditional code exploits, coercing victims into handing over funds or two-factor verification codes voluntarily.
Google announced this sweeping security rollout during its global briefing at 9:00 AM PT / 12:00 PM ET / 16:00 GMT, positioning machine learning directly inside communication pipes.
The centerpiece of this update is the opt-in Enhanced Protection switch rolling out inside Google Messages.
When activated, the system evaluates suspicious exchanges with unknown contacts by deploying cloud-based Gemini architectures inside a secure, hardware-isolated enclave dubbed Private AI Compute.
This cloud processing allows the system to recognize manipulative dialogue patterns that smaller on-device models frequently miss.
To protect personal privacy, the underlying data remains fully encrypted end-to-end so that nobody, not even system engineers, can read message contents.
Meanwhile, on-device intelligence handles link protection through Gemini Nano to inspect unfamiliar web addresses against real-time network signals.
Phishing rings often spin up disposable fraudulent domains within minutes, bypassing static reputation databases before security researchers can flag them.
By pairing local heuristic evaluation with on-device heuristics, the system intervenes before malicious code or credential-harvesting pages load in the browser.
Beyond textual fraud, voice networks remain a primary vector for financial theft.
Official internal metrics show that system-level scam detection tools actively intercept more than 5 million suspicious calls and messages every month.
In regions where banking impersonation surged, an automated verification handshake trial intercepted over 3 million fraudulent bank calls in under four months.
Fraudsters routinely manipulate targets into typing specific MMI dialing codes (such as *21*) to silently divert incoming calls and capture two-factor SMS authentication codes.
The upcoming dialer framework actively alerts users to manual forwarding inputs and prevents sideloaded background applications from altering forwarding rules without explicit consent.
Additionally, screen-sharing defenses are expanding across mobile web browsers.
Beginning with devices running Android 15 or newer, the system automatically masks sensitive financial fields, payment cards, and password inputs whenever a user shares their display.
| Feature Layer | Primary Technology | Privacy Architecture | Hardware Availability |
|---|---|---|---|
| Enhanced Message Protection | Cloud Gemini Models | Private AI Compute (Encrypted) | Pixel 6+, Galaxy S24+, AICore Phones |
| Real-Time URL Shield | Gemini Nano | 100% On-Device Processing | Pixel 10+, Galaxy S26, Foldables |
| Screen-Share Obfuscation | Android System Sandbox | Local OS Rendering Hook | Android 15 and Newer |
| Call Forwarding Guard | Telephony API Interceptor | Local MMI Verification | Pixel Series & Select Flagships |
| Verified Financial Calls | Carrier & Bank API Handshake | Real-Time Telco Routing | Expanding Global Markets |
The technical execution demonstrates how Google balances device-level computational constraints against cloud model capabilities.
While basic text pattern matching runs efficiently on low-power chips, dissecting psychological coercion requires extensive contextual comprehension.
By offloading difficult semantic evaluation to Private AI Compute, older flagships gain access to high-parameter fraud detection without killing battery performance.
However, the hardware tiering creates an undeniable fragmentation gap.
Cutting-edge link analysis powered by local neural engines remains locked to premium chipsets with dedicated hardware accelerators.
The broader telecommunications industry faces relentless pressure as carrier-level SMS filters fail to halt sophisticated fraud networks.
By deploying active Google AI anti-scam protections at the core operating system layer, Google forces rival smartphone ecosystems to adopt proactive, automated defense mechanisms.
Modern phishing does not rely on crude spelling errors anymore; it uses polished corporate jargon, convincing synthetic voices, and coordinated pressure tactics.
Relying on human vigilance to catch every fraudulent message is an outdated security strategy that leaves regular users exposed.
Google deserves credit for building client-side safety nets that step in before someone empties their life savings over a fake delivery alert.
Still, giving cloud infrastructure even encrypted access to unlisted conversations will make privacy purists hesitate before flipping the toggle.
Turning security into an opt-in toggle feels like a defensive compromise rather than a decisive blow against cybercrime syndicates.
If the technology is genuinely airtight and private, it should safeguard everyone right out of the box.
- K.K., Founder of TechKomo